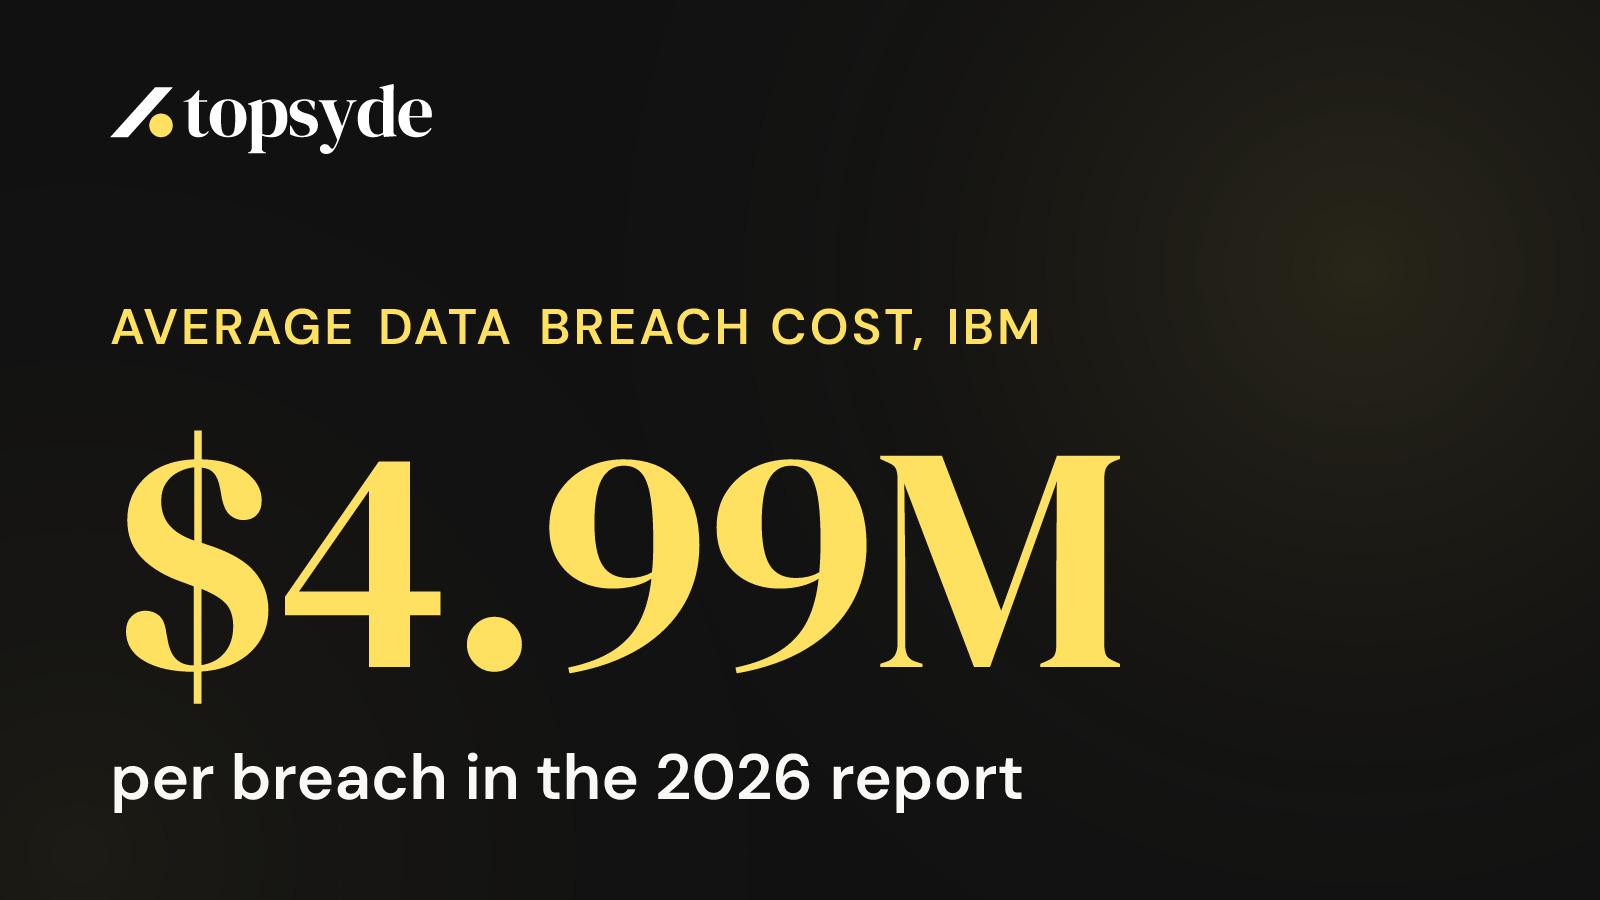

A data breach costs organizations an average of $4.99 million per incident according to IBM's 2026 Cost of a Data Breach Report, the highest figure in the report's history. That average covers all breaches and skews toward large organizations, but it includes immediate cleanup costs, lost revenue, legal fees, regulatory fines, and long-term reputation damage that can devastate small to medium businesses.
What Does a WordPress Security Breach Actually Cost?
A WordPress security breach goes far beyond the few thousand dollars you'll pay a security firm to clean malware. The larger cost comes from business disruption, lost customer trust, and cascading effects that can persist for years.
IBM's Cost of a Data Breach Report splits the average total cost into four categories:
- Detection and escalation
- Notification costs
- Post-breach response
- Lost business
In the 2026 report, detection, escalation and lost business together accounted for most of the $4.99 million average.
The timeline matters too. IBM's reports have consistently found that breaches contained in under 200 days cost roughly a million dollars less than those that drag on longer. Most WordPress site owners discover breaches through customer complaints or Google warnings, not through proactive monitoring, so the clock has usually been running for a while before anyone notices.
Where the Money Goes When a WordPress Site Is Hacked
The invoice from whoever cleans the site is the line everyone budgets for. It is rarely the biggest one. Here is what a breach actually touches, by the kind of site you run.
An online store that leaks customer data
A WooCommerce store compromised through an outdated plugin can expose names, addresses and order details, and a checkout skimmer can capture card numbers as they are typed. Beyond the cleanup, you are looking at a forensic investigation your payment processor will expect, legal review of your notification duties, the cost of notifying every affected customer, and a conversion rate that stays depressed for months because shoppers who were warned by their bank do not come back quickly.
A service business that gets flagged by Google
A marketing agency's WordPress site infected with malware that redirects visitors to phishing pages gets flagged by Google Safe Browsing. Every browser shows a red warning page in front of the agency's own portfolio. The site is effectively offline for however long the cleanup and Google's review take, prospects who were about to sign see the warning instead, and existing clients start asking whether their own sites are safe in your hands.
A professional firm that exposes client records
A law or accounting firm's site compromised through a vulnerable form plugin can expose intake forms, uploaded documents and contact details. That brings professional-conduct obligations, client notification, cyber-insurance deductibles and the quiet loss of clients who decide to take their files somewhere else.
In each case the pattern is the same. The technical cleanup is the cheap, fast part. Lost business, notification and legal review are the expensive, slow part, and they land on businesses that were often saving a few dollars a month on hosting.
Why Prevention Costs So Much Less Than Recovery
Here's the comparison that should keep every business owner awake at night.
Managed WordPress hosting with security built in costs $89 a site a month with TopSyde, or $1,068 a year. A professional cleanup of a hacked site alone typically runs into the thousands, and the lost business, notification and legal costs that follow a data breach can run into the hundreds of thousands. You do not need a precise multiplier to see that one year of prevention costs less than one week of recovery.
The point is not that managed hosting makes a breach impossible. Nothing does. The point is that daily scanning, prompt updates, a firewall and tested backups shrink both the odds of a breach and the time it takes to find one, and time to detection is the single biggest driver of breach cost in IBM's data.
What Managed WordPress Hosting Security Actually Includes
Most business owners don't realize that DIY WordPress security is like performing surgery on yourself. You might save money upfront, but the expertise gap creates catastrophic risk.
Here is what TopSyde includes on every site:
- TopSyde Sentinel scans every site daily over SSH from outside the site, so malware cannot hide from it the way it hides from a plugin running inside WordPress
- Core and wordpress.org plugin files are checked against official checksums, and the scan hunts for backdoors, hidden admin users, application-password keys and SEO spam
- Clear high-confidence threats are quarantined automatically. Anything less certain waits for staff review. Files are quarantined, never deleted, so a wrong call can be undone
- Every plugin, theme and WordPress update is backed up first, health-checked after, and rolled back on its own if a page breaks
- Cloudflare firewall and CDN in front of every site, free SSL, a two-factor login switch and form spam protection
- Daily backups kept 30 days with one-click restore
- Cleanup of a site that is already infected is included, even during the free trial
And a response you can plan around:
- A site that is down is answered within 15 minutes, 24 hours a day, 7 days a week
- A broken checkout, login or form is answered within 1 hour during business hours
- Everything else within 1 business day
- A 99.9% monthly uptime guarantee with service credits, in writing on the SLA page
One honest note on compliance. TopSyde does not sell PCI, GDPR or SOC 2 compliance as a service. The infrastructure under every site, Kinsta on Google Cloud plus Cloudflare, is SOC 2 certified, which helps when you fill in a vendor questionnaire, but your own compliance obligations remain your own.
Compare this to DIY security where you're responsible for:
- Installing and configuring security plugins correctly
- Staying current on the steady stream of WordPress plugin vulnerabilities
- Monitoring logs and identifying threat patterns
- Responding to incidents at 2 AM on weekends
One misconfigured security plugin or delayed update creates the vulnerability that costs you months of recovery.
The Hidden Cost: Business Owner Stress and Productivity
Beyond dollars, security breaches exact a toll that's rarely quantified. A hacked site means weeks of interrupted work, awkward conversations with customers, and a nagging distrust of every technology decision that follows.
The peace of mind factor counts for something. When TopSyde handles your WordPress security, you're not waking up to Google Safe Browsing warnings or customer emails about weird redirects. You're focusing on what you do best: growing your business.
Smart Prevention Strategies That Work
These are the prevention measures that close the doors attackers actually use.
Basic protection, the floor every site needs:
- Managed WordPress hosting with security built in
- Core, plugin and theme updates applied promptly, with a backup taken first and a rollback path if something breaks
- Daily backups stored away from the site
- SSL certificate and forced HTTPS
Stronger protection, worth it for any site that takes money or holds customer data:
- A web application firewall in front of the site
- Two-factor authentication for all admin accounts
- Daily server-side malware scanning with a human reviewing anything uncertain
- Removing every plugin and theme you do not use
Every item on both lists is included in TopSyde hosting at $89 a site a month, with volume pricing from 11 sites. Compare that to a single professional cleanup, before any lost business is counted.
Why DIY Security Fails for Business Owners
When businesses try to handle WordPress security themselves, the same four things go wrong:
- Knowledge gap. WordPress security requires understanding server configuration, PHP vulnerabilities, database hardening, and shifting attack patterns. Most business owners lack this expertise.
- Time investment. Proper security monitoring requires 2-3 hours weekly. That's $20,000+ annually for a business owner billing $200/hour.
- Update complexity. WordPress releases security updates irregularly. Plugin updates can break functionality, requiring immediate testing and rollback capabilities.
- Incident response. When attacks happen at 11 PM on Sunday, DIY security means you're troubleshooting alone while your site bleeds revenue.
The WordPress security best practices guide we published covers technical implementation, but the business reality is simpler: outsource security to experts who do it full-time.
Calculating Your Business's Real Risk
Use this framework to think about what a breach would cost your business.
Revenue exposure:
- E-commerce site: every hour offline is lost sales, and a data leak depresses conversions for months afterward
- Lead generation site: every day flagged by Google is a day of leads that go to a competitor
- Brochure or portfolio site: the direct loss is smaller, but the reputational hit with the clients who find the warning page is not
Data exposure:
- Healthcare, legal, financial: notification duties, professional-conduct obligations and regulators get involved
- B2B services with client data: your clients' trust, and sometimes their contracts, are on the line
- Local business with contact forms only: the cheapest breach to recover from, and still weeks of disruption
Add up a realistic number for a week of lost business, the cost of telling every affected customer, and the professional fees to review your obligations. Then set that against the annual cost of hosting that includes daily scanning, firewall, backups and a team that answers when something breaks.
Making the Business Case for Managed WordPress Security
When presenting security investment to stakeholders, frame it as business insurance rather than an IT expense.
On risk mitigation, it reduces the odds of a business interruption and shortens the one you do have, protects customer relationships and lifetime value, and maintains your competitive position in the market.
On opportunity cost, it frees up 2-3 hours weekly for revenue-generating activities, eliminates emergency response stress and productivity loss, and lets you focus on growth instead of crisis management.
There's a competitive angle too. Customer trust becomes a differentiator, you can collect customer data for marketing with confidence, and you're able to expand into regulated industries.
The managed WordPress hosting cost breakdown looks at these numbers further, but the core message remains: security investment pays for itself through prevented losses and enabled growth.
Keep Reading on TopSyde
- Small Business Website Checklist: 15 Critical Mistakes to Avoid: Most small business websites fail at basics like SSL, mobile optimization, and backups. This checklist covers 15 costly mistakes and how to fix them.
- How to Clean a Hacked WordPress Site (The Right Way): Why in-WordPress scanners miss reinfections, and how server-layer scanning closes the gap.
- What AI-Powered WordPress Monitoring Actually Does: Where AI helps a managed host catch problems, and where human review still decides.
- Managed hosting for individual site owners
- TopSyde pricing
Frequently Asked Questions
How quickly do WordPress security breaches typically get detected?
Breaches took 247 days on average to identify and contain in IBM's 2026 research, which covers all breaches rather than WordPress alone. Business owners usually discover them through customer complaints, Google warnings, or dramatic traffic drops rather than proactive monitoring. On TopSyde, Sentinel scans every site daily from outside the site, uptime is checked every 5 minutes, and a site that is down is answered within 15 minutes at any hour.
What's the real difference between $20/month shared hosting security and managed WordPress security?
Shared hosting provides basic malware scanning and backups, but you're responsible for updates, configuration, and incident response. Managed WordPress hosting includes daily server-side scanning, updates that are backed up and health-checked, a web application firewall, and people who answer when something breaks. The expertise gap, not the server, is what separates the two.
Can small businesses recover from major WordPress security breaches?
Yes, but recovery takes far longer than the cleanup. Rebuilding customer trust and search rankings after a Google warning or a data leak is measured in months, and the lost business during that period usually dwarfs the technical bill. Prevention is cheaper than winning those customers back.
How do I justify managed WordPress hosting costs to budget-conscious stakeholders?
Frame it as business insurance. Roughly $1,000 a year of hosting with security built in, set against a cleanup that runs into the thousands and lost business that can run far higher. You wouldn't skip liability insurance to save $1,000 annually, and for a business that depends on its website, a compromise is a more likely event than a fire or a flood.
What should I look for in a managed WordPress hosting security package?
Look for daily server-side malware scanning, a clear answer on how removal works and whether it can be undone, a web application firewall, daily backups with easy restoration, SSL certificates, and a written response time for a site that is down. TopSyde's Sentinel scanner and SLA cover all of these at $89 a site a month, less than one day's revenue loss from a typical breach.
DevOps & Security Lead
12+ years DevOps, Linux & cloud infrastructure certified
Marcus leads infrastructure and security at TopSyde, managing the server fleet and AI monitoring systems that keep client sites fast and protected. Former sysadmin turned WordPress hosting specialist.